The transimpedance amplifier presents a low impedance to the sensor and isolates it from the output voltage of the operational amplifier. In its simplest form (Fig. 1), a transimpedance amplifier is just an opamp with a large-valued feedback resistor, R f.OverviewIn, a transimpedance amplifier (TIA) is a to converter, almost exclusively implemented with one or more (opamps). The TIA can be used to amplify the current output of In the circuit shown in Figure 1, a sensor (represented as a current source) such as a photodiode is connected between ground and the inverting input of the opamp. The other input of the opamp is also connected to ground,. The frequency response of a transimpedance amplifier is inversely proportional to the gain set by the feedback resistor. The sensors which transimpedance amplifiers are used with usually hav.
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. This guide evaluates the 10 best network security solutions for 2026, detailing technical specifications, key strengths, purchase rationale, and unique capabilities for global enterprises, mid-market growth companies, and hybrid workforces.
You can create, filter, modify, or delete IPS signatures on the IPS Policy Signatures page in Security Director. The intrusion prevention system (IPS) compares traffic against signatures of known threats and blocks traffic when a threat is detected. To detect such activity, IPS uses signatures. government repository of standards based vulnerability management data represented using the Security Content Automation Protocol (SCAP). The NVD includes databases of security. Many firewall manufacturers can provide the IDS / IPS module with an additional license in their products. Snort can be deployed inline to stop these. These databases store unique threat signatures,malware patterns, virus definitions, intrusion fingerprints,that security tools rely on to spot malicious activity.
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. Effective security systems have multiple layers, like an onion.
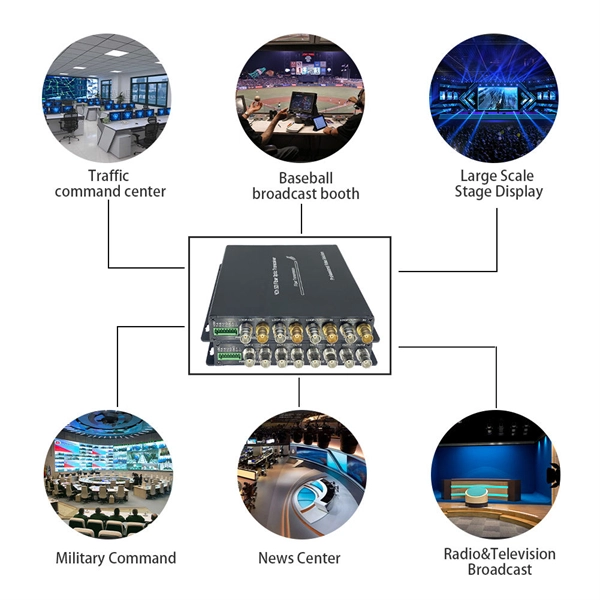
You'll get the precise, standardized dimensions of a 1U server rack unit — including height (1. 45 mm), width (19″ / 48. 26 cm), mounting hole spacing, and critical clearance allowances — plus actionable guidance on verifying physical fit, avoiding common installation. The IPC-C1E-BAR30-RH-N1 is an entry-level 1U appliance chassis with 15” depth for space-sensitive applications, such as Network & Security appliance, firewall, VPN, Telephony and military applications. 6” x 12”) motherboard can be populated into this appliance chassis. reserves the right to make any final modifications. For example, a typical full-size rack cage is 42U high, while equipment is typically 1U, 2U, 3U, or 4U high.
Network security audits help protect sensitive data by evaluating access controls, identifying security weaknesses such as open ports or outdated software, monitoring unauthorized activity, and ensuring compliance with data protection regulations such as GDPR or PCI DSS. This blog is about the top 10 network security testing methodologies that every cybersecurity professional should adopt in 2025. By learning and implementing these, organizations can strengthen their defenses and stay safe from attackers. The sophistication level of cyberattacks is staggering. public companies must disclose any cybersecurity incident they determine to be 'material' within four business days of that determination. Meanwhile, the average. Regular testing, integration with DevOps/CloudOps, combining automation with human expertise, and partnering with experts like Zymr, ensure enterprises stay resilient against evolving AI-driven and cloud-focused threats. Critical areas to focus on include evaluating firewalls, access controls, encryption methods, network segmentation, and patch management.
[PDF Version]
In this comprehensive guide, we'll walk you through each stage of the process, from understanding why business owners decide to sell, to preparing your company for the market, determining its value, finding qualified buyers, and managing negotiations through to closing. Selling your security systems installation business is a major decision, and knowing where to start can be challenging. Businesses often encounter challenges in handling excess technology, especially when it comes to pre-owned networking devices. Implementing best practices ensures that these devices are sold. Enterprises replacing networking hardware end up with surplus devices, including routers, switches, firewalls, and storage units. Holding onto these assets can occupy valuable space and tie up resources that could be better deployed. What you need is a network equipment.
The SFP-10G-AOC SFP+ Active Optical Cable is a plug-and-play, cost-effective solution for 10Gbps connections. It uses Multi-Mode Fiber (MMF) with SFP+ connectors and has built-in optics, eliminating the need for separate transceivers and patch cables. DESIGNED FOR USE IN 10GB/S DATA RATE LINKS. COMPLIANT WITH 10G ETHERNET AND CPRI Amphenol's 10G SFP+ optical modules include SFP+ AOC. They are compliant with SFP+ MSA, SFF-8431 and SFF-8472, and are mainly used in Telecom, Wireless, InfiniBand, and Fiber Channel. AOCs are much thinner and lighter than copper cables, which makes cabling easier. 10Gtek. 10G SFP+ AOC (Active Optical Cables) are conceptually two SFP+ optical transceivers with a fiber optic cable permanently embedded into each end (the fiber cable cannot be removed). Whether you're upgrading server‑to‑switch links, extending. Pivotal Optics' Active Optical Cables (AOCs) are fully integrated, plug-and-play fiber assemblies designed for short- to medium-range high-speed data links—without the need for separate transceivers. Built with bonded multi-mode or single-mode fiber, these cables deliver secure, low-latency.
[PDF Version]Contact us for competitive quotes on any of our power communication and smart grid products
Get a Quote