Network security audits help protect sensitive data by evaluating access controls, identifying security weaknesses such as open ports or outdated software, monitoring unauthorized activity, and ensuring compliance with data protection regulations such as GDPR or PCI DSS. This blog is about the top 10 network security testing methodologies that every cybersecurity professional should adopt in 2025. By learning and implementing these, organizations can strengthen their defenses and stay safe from attackers. The sophistication level of cyberattacks is staggering. public companies must disclose any cybersecurity incident they determine to be 'material' within four business days of that determination. Meanwhile, the average. Regular testing, integration with DevOps/CloudOps, combining automation with human expertise, and partnering with experts like Zymr, ensure enterprises stay resilient against evolving AI-driven and cloud-focused threats. Critical areas to focus on include evaluating firewalls, access controls, encryption methods, network segmentation, and patch management.
[PDF Version]
This document provides the overall architecture for Deterministic Networking (DetNet), which provides a capability to carry specified unicast or multicast data flows for real-time applications with extremely low data loss rates and bounded latency within a network domain. ● Other distribution automation applications such as Direct Transfer Trip. Our engineers are experts at multifunction microprocessor-based relay technology, and we design protection schemes for generation, transmission, distribution, and low-volt ge systems worldwide. Of particular concern is the potential for cyberattacks that exploit high-wattage IoT devices, such as EV chargers, to manipulate local demand and destabilize the grid. With tools ranging from intent-based networking to policy-driven orchestration and multi-cloud integration, these leading. The handbook describes various power distribution system constructions and elements there-of, technical considerations, distribution automation infrastructure and functionality, communication aspects, special automation applications and life cycle aspects.
[PDF Version]
You can create, filter, modify, or delete IPS signatures on the IPS Policy Signatures page in Security Director. The intrusion prevention system (IPS) compares traffic against signatures of known threats and blocks traffic when a threat is detected. To detect such activity, IPS uses signatures. government repository of standards based vulnerability management data represented using the Security Content Automation Protocol (SCAP). The NVD includes databases of security. Many firewall manufacturers can provide the IDS / IPS module with an additional license in their products. Snort can be deployed inline to stop these. These databases store unique threat signatures,malware patterns, virus definitions, intrusion fingerprints,that security tools rely on to spot malicious activity.
In this comprehensive guide, we'll walk you through each stage of the process, from understanding why business owners decide to sell, to preparing your company for the market, determining its value, finding qualified buyers, and managing negotiations through to closing. Selling your security systems installation business is a major decision, and knowing where to start can be challenging. Businesses often encounter challenges in handling excess technology, especially when it comes to pre-owned networking devices. Implementing best practices ensures that these devices are sold. Enterprises replacing networking hardware end up with surplus devices, including routers, switches, firewalls, and storage units. Holding onto these assets can occupy valuable space and tie up resources that could be better deployed. What you need is a network equipment.
They power essential devices like security cameras, access points, and VoIP phones without the need for extra wiring. Rather than utilizing a wireless network that can be hacked through any number of online devices, PoE transmits data via one cable that cannot be attacked unless there is a direct, wired connection. It eliminates the need for separate power supplies, thus helping to streamline installation and reduce clutter. With this, PoE offers more flexibility. I've researched the top PoE network switches of 2025 and found excellent options for different needs, from compact unmanaged models to powerful managed switches with high PoE budgets. If you're looking for a. If you're building or upgrading a video surveillance network, one of the most important components to get right is your PoE (Power over Ethernet) switch. It compares PoE with WiFi and.
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. This guide evaluates the 10 best network security solutions for 2026, detailing technical specifications, key strengths, purchase rationale, and unique capabilities for global enterprises, mid-market growth companies, and hybrid workforces.
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. Effective security systems have multiple layers, like an onion.
The Logs section provides the tools to view the system logs, authentication logs and auditing logs as well as download the logs in CSV format. Firewall logs can be used by the administrator for troubleshooting network. You can access the system logs by. A security information and event management (SIEM) solution ensures a healthy security posture for an organization's network by monitoring different types of data from the network. Think of logs as breadcrumbs that show everything happening across your routers, switches, firewalls, and other network infrastructure. This includes considerations for configuring the logging settings for different policies, the configuration of local log storage databases, and setting both local logging for the Firewall. A log is an automatically generated, time-stamped file that provides an audit trail for system events on the firewall or network traffic events that the firewall monitors. In this comprehensive guide, we will cover the key concepts, tools, and techniques for analyzing log. Alternate format: Network security logging and monitoring - ITSAP.
[PDF Version]
There are 8 steps to managing your network's security including: Be Organized. Develop and enforce a strong password policy. Ensure firewalls are properly configured. It implements security measures, policies, and tools that safeguard the entire network infrastructure to achieve the goal. This framework establishes best practices for device authentication, firmware updates, and real-time monitoring to detect potential threats. Develop data. This Security Requirements Guide (SRG) is published as a tool to improve the security of Department of Defense (DOD) information systems.
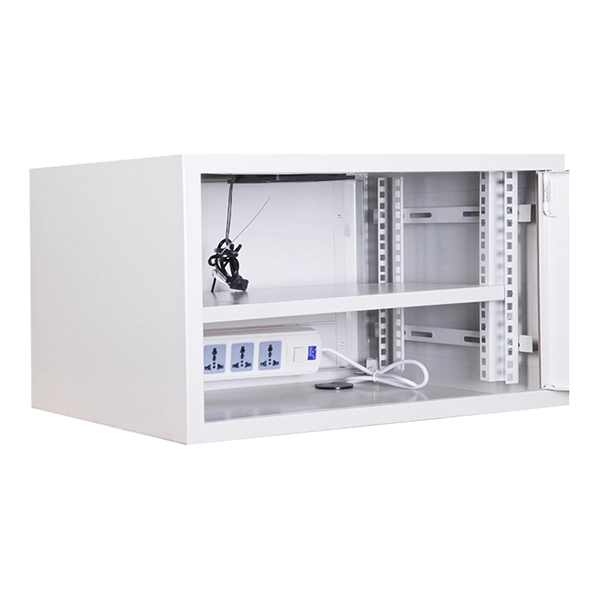
A server rack typically draws between 10-60 amps, depending on its power density, hardware type, and configuration. Kilowatt per rack (kW/rack) is the power assigned to a server rack in a data center. Always calculate amperage using P=V×I and consult. The power demands of server racks can be influenced by several factors, including the number and type of servers, networking equipment, storage devices, and other peripherals. The power requirements of server racks are typically measured in terms of voltage (V), current (A), and power rating. One of the critical parameters for running data centre operations is the kilowatt rating for the power usage at the server rack level. Having some understanding of your rack's power consumption allows you to balance your load, optimize your IT infrastructure, and ensure adequate cooling and power. To help, we have created a handy server rack power consumption calculator tool to help you. Using the steps below, you can see how we made these calculations and understand where the results in the Server Rack Power Consumption Calculator are coming from.
[PDF Version]Contact us for competitive quotes on any of our power communication and smart grid products
Get a Quote