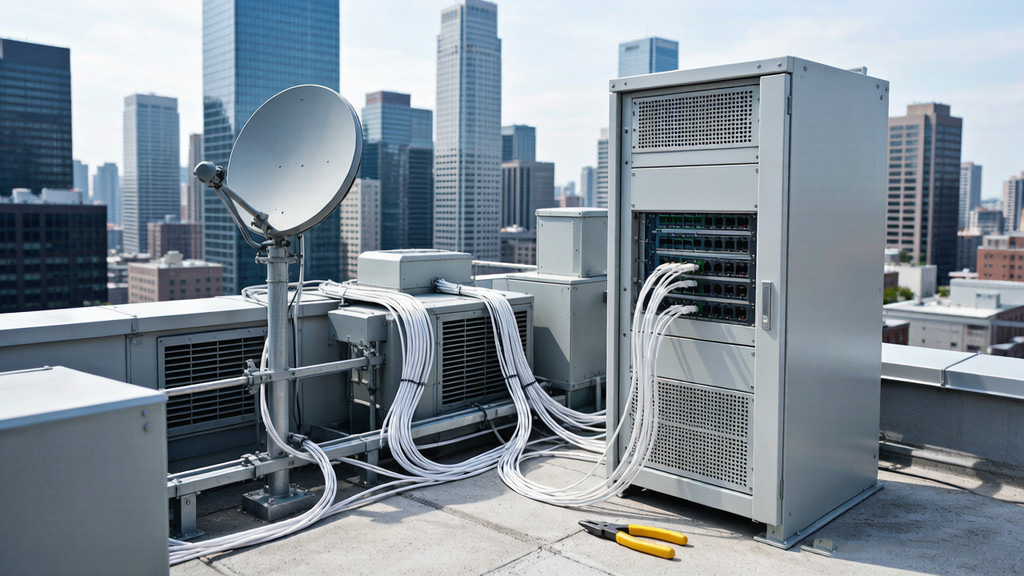
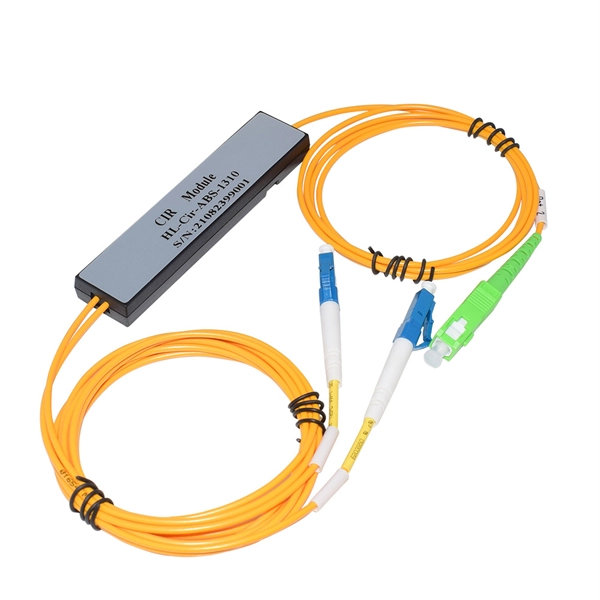
This comprehensive guide provides a step-by-step deep dive into how to rack and organise network equipment properly, covering network cabinets, open racks, PDUs, patch panels, cable management, airflow, labelling, and future-proofing. A Network Cabinet, often interchangeably called a server rack, is a physical frame or enclosure designed to house and organize various types of network hardware and accessories. The primary purpose of a network. Network cabinet placement and wiring tips Many network devices are stored in the cabinets. We will discuss the. When designing a data center, the first step is to choose the right type of rack for your particular use case. Whether you need it for an office. In this article we talk about proper placement of equipment in a rack, in other words, we take a systematic look at the operation of a server rack: from drawing up a plan and installation to wiring labeling. The entire narrative is based primarily on my experience as a data center engineer, and.
[PDF Version]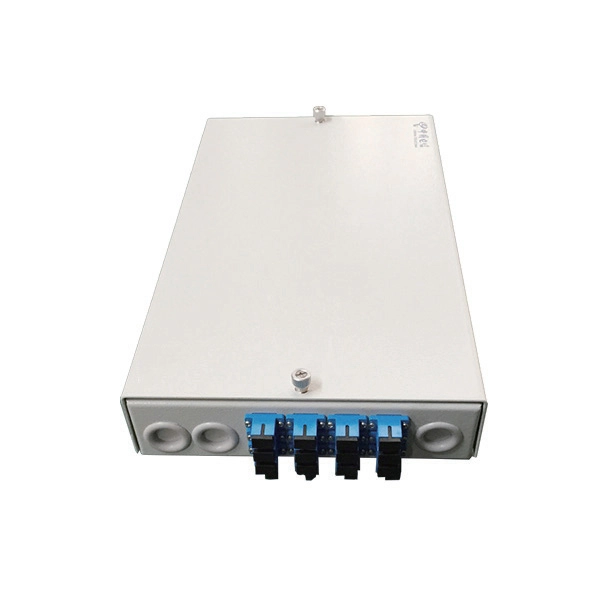
The DSY-D6000 distribution network automation control terminal (DTU) is a monitoring terminal product developed for the increasingly widespread application of ring main units and small switching stations in urban power grids. Advanced intelligent equipment is needed to improve the distribution network. It can work in conjunction with the main station and substation systems. Distribution Automation Terminals (DTU and FTU) by Application (Substation, Pole Mounted Switch, Distribution Transformer, Others), by Types (Distribution Terminal Unit (DTU), Feeder Terminal Unit (FTU)), by North America (United States, Canada, Mexico), by South America (Brazil, Argentina, Rest of. The ZT-D30 Distribution Automation Substation Terminal DTU is primarily applied in distribution automation systems. It can be coordinated with. With complex working environments, large scales of circuits, wide varieties of equipment, traditional medium-voltage distribution network (10kV ~ 35kV) plays a significant role in power transmission, requiring high reliability and stability to guarantee the safety. It offers robust stability, high reliability, excellent real-time.
[PDF Version]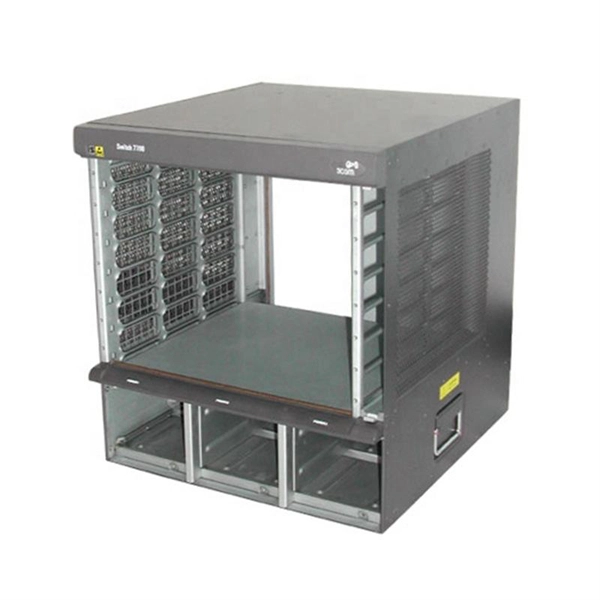
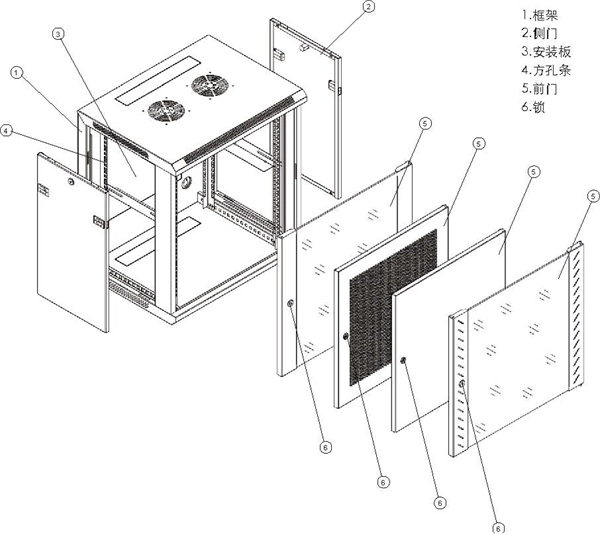
The network cabinet is a closed metal structure that houses network equipment like routers, switches, patch panels, servers, energy distribution equipment, as well as cables management equipment. Not only a simple storage unit, a network cabinet is a key player in safeguarding and organizing critical network equipment. Whether you're setting up a new office or streamlining an existing network, understanding the importance, types, and usage of network cabinets is crucial. It follows standardized rack dimensions, most commonly 19-inch rack width, making it compatible with global IT equipment standards. This article provides a simple guide to.
The Logs section provides the tools to view the system logs, authentication logs and auditing logs as well as download the logs in CSV format. Firewall logs can be used by the administrator for troubleshooting network. You can access the system logs by. A security information and event management (SIEM) solution ensures a healthy security posture for an organization's network by monitoring different types of data from the network. Think of logs as breadcrumbs that show everything happening across your routers, switches, firewalls, and other network infrastructure. This includes considerations for configuring the logging settings for different policies, the configuration of local log storage databases, and setting both local logging for the Firewall. A log is an automatically generated, time-stamped file that provides an audit trail for system events on the firewall or network traffic events that the firewall monitors. In this comprehensive guide, we will cover the key concepts, tools, and techniques for analyzing log. Alternate format: Network security logging and monitoring - ITSAP.
[PDF Version]
A typical full-size rack is 42U, which means it holds just over 6 feet (180 cm) of equipment, and a typical "half-height" rack is 18U–22U, which is around 3 feet (91 cm) high. The mounting-hole distance (as shown to the right) differs for 19-inch racks and 23-inch racks: 19-inch racks use uneven spacings (as shown to the right) while 23-inch.
Network security audits help protect sensitive data by evaluating access controls, identifying security weaknesses such as open ports or outdated software, monitoring unauthorized activity, and ensuring compliance with data protection regulations such as GDPR or PCI DSS. This blog is about the top 10 network security testing methodologies that every cybersecurity professional should adopt in 2025. By learning and implementing these, organizations can strengthen their defenses and stay safe from attackers. The sophistication level of cyberattacks is staggering. public companies must disclose any cybersecurity incident they determine to be 'material' within four business days of that determination. Meanwhile, the average. Regular testing, integration with DevOps/CloudOps, combining automation with human expertise, and partnering with experts like Zymr, ensure enterprises stay resilient against evolving AI-driven and cloud-focused threats. Critical areas to focus on include evaluating firewalls, access controls, encryption methods, network segmentation, and patch management.
[PDF Version]Contact us for competitive quotes on any of our power communication and smart grid products
Get a Quote