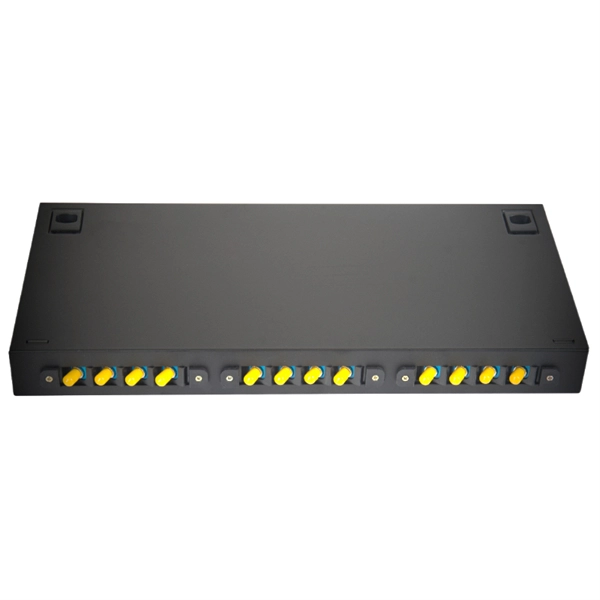
In a typical enterprise network architecture, the access layer switch is the first point of contact between end-user devices and the rest of the network. Access. The term campus LAN refers to a LAN network that spans a single geographic location, such as a building or university campus. An enterprise network is a large network that may contain several campus networks spanning different. The hierarchy Ethernet network is a three-layer integrated setup of networking devices.
Missing VLANs on switches: A port may become dormant if a VLAN associated with it is removed. Native VLAN Mismatch: When a switch's interfaces have distinct native VLANs, untagged traffic may be diverted. Cisco Discovery Protocol errors occur when native. A VLAN on Cisco switches segments a physical switch into multiple logical broadcast domains by assigning ports to VLANs. VLANs improve network management and require routing for inter-VLAN communication The. Switchport mode access is essential for configuring network devices in environments where end devices (e., computers, printers) connect to a switch. These ports are typically placed in “access” mode to carry traffic for a single VLAN. In a real network, you also need to assign access ports, configure trunk links, verify forwarding behavior, and avoid common mistakes such as native VLAN mismatches, overwritten trunk VLAN lists, or inactive SVIs. On. In order to find and fix connectivity problems caused by Virtual Local Area Networks (VLANs), VLAN troubleshooting entails a methodical approach to examining the setup and condition of network devices.
[PDF Version]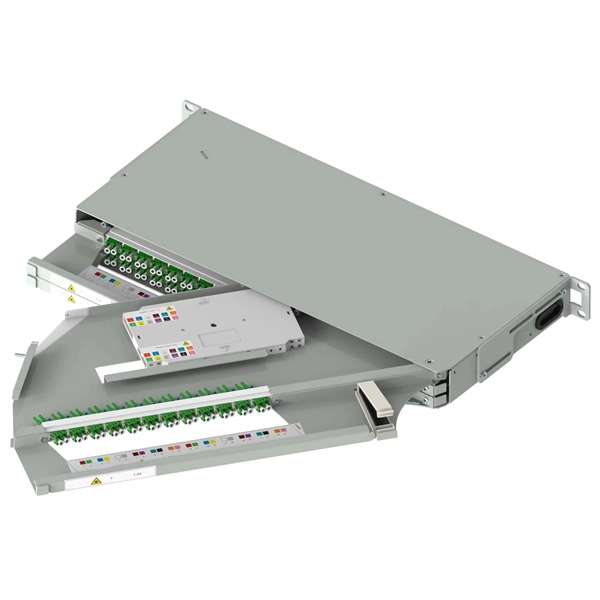
Switch stacking is a feature of certain Cisco access layer switches which allows for the creation of a single logical device from many individual devices via a backside stack port connected by several stack cables. Stackable switches logically to become one switch. While they both aim to simplify switch management and enhance resilience, they work in different ways and serve different use. Switch stacking is a technology that connects multiple physical switches via dedicated high-speed cables, virtualizing them into a single logical switch. This logical switch features a unified management IP address, a single configuration file, and shared forwarding tables (such as MAC address.
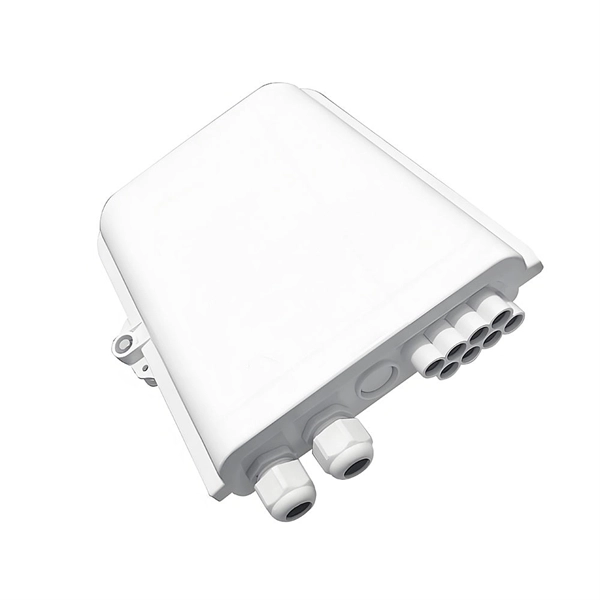
Networking hardware typically refers to equipment facilitating the use of a computer network. Typically, this includes routers, switches, access points, network interface cards and other related hardware. This is a list of notable vendors who produce network hardware. Routers• • - acquired by •. • • AirPro• - acquired by •. • • - acquired by • •. • • (includes former Solarflare and )• (includes former Avago and Emulex)•.
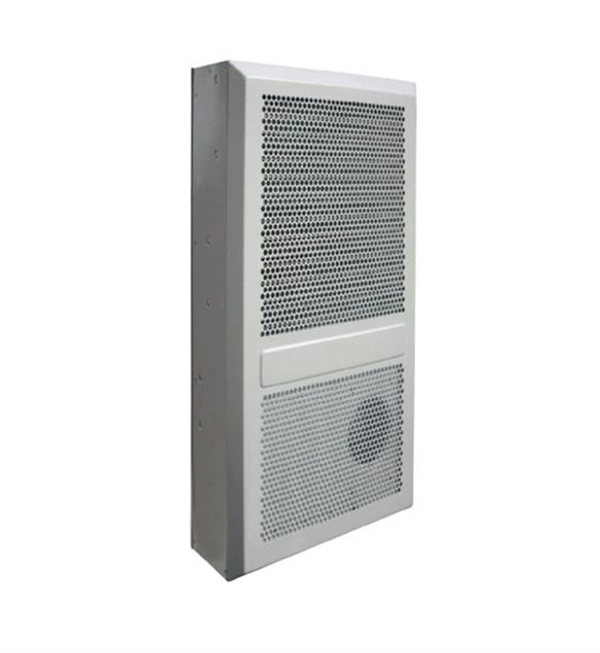
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. Effective security systems have multiple layers, like an onion.
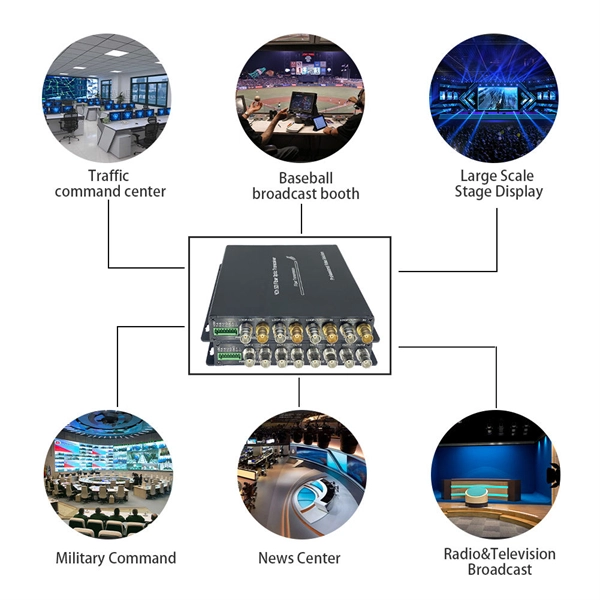
You'll get the precise, standardized dimensions of a 1U server rack unit — including height (1. 45 mm), width (19″ / 48. 26 cm), mounting hole spacing, and critical clearance allowances — plus actionable guidance on verifying physical fit, avoiding common installation. The IPC-C1E-BAR30-RH-N1 is an entry-level 1U appliance chassis with 15” depth for space-sensitive applications, such as Network & Security appliance, firewall, VPN, Telephony and military applications. 6” x 12”) motherboard can be populated into this appliance chassis. reserves the right to make any final modifications. For example, a typical full-size rack cage is 42U high, while equipment is typically 1U, 2U, 3U, or 4U high.
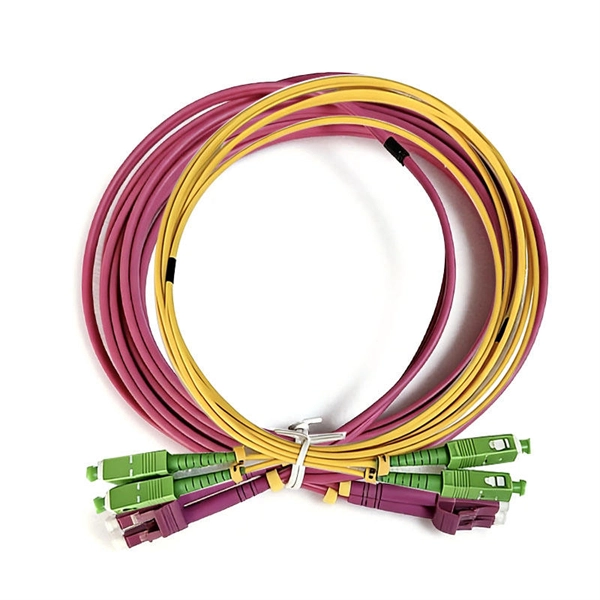
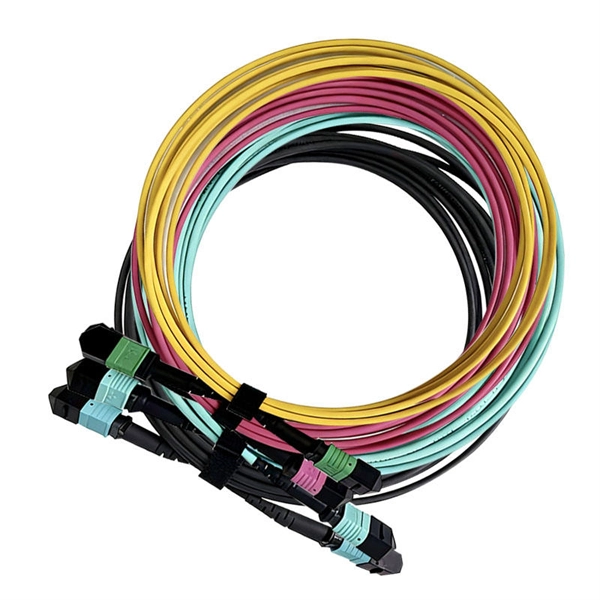
Our hybrid powered cable transmits data and power in one cable, ideal for powering security cameras, Wi-Fi access points, and more, eliminating the need for separate data and power lines. Uninterrupted monitoring of large infrastructure for increased safety and targeted preventative maintenance. Various cable constructions within the portfolio offer unlimited. CommScope bundles hybrid cabling to your custom specifications, using our high-performance fiber-optic, unshielded twisted pair and coaxial cables. ActiFi is a Class 3‑rated composite cable that supports low‑voltage (Class 2, 57 VDC/100 V) as well as bulk power solutions.
Network security audits help protect sensitive data by evaluating access controls, identifying security weaknesses such as open ports or outdated software, monitoring unauthorized activity, and ensuring compliance with data protection regulations such as GDPR or PCI DSS. This blog is about the top 10 network security testing methodologies that every cybersecurity professional should adopt in 2025. By learning and implementing these, organizations can strengthen their defenses and stay safe from attackers. The sophistication level of cyberattacks is staggering. public companies must disclose any cybersecurity incident they determine to be 'material' within four business days of that determination. Meanwhile, the average. Regular testing, integration with DevOps/CloudOps, combining automation with human expertise, and partnering with experts like Zymr, ensure enterprises stay resilient against evolving AI-driven and cloud-focused threats. Critical areas to focus on include evaluating firewalls, access controls, encryption methods, network segmentation, and patch management.
[PDF Version]
Discover 5 key features of high-performance industrial switches for Industry 4. 0—boosting reliability, security, and real-time data in smart manufacturing. As a core hub, the performance of industrial switches is related. Elevate your industrial operations with an AI-ready, rugged network that offers peak performance, high resilience, advanced security—and that smoothly integrates IT proficiencies into OT environments. Network Segmentation: Industrial switches support network segmentation through technologies like Virtual Local Area Networks (VLANs). By. Industrial switches are the backbone of modern factories and automated systems, powering equipment, connecting machines to critical networks, and enabling vital communication between different components across the floor. Today's advanced manufacturing techniques like robotics, machine vision, and. What Are the Key Features and Benefits of a Cisco Industrial Switch? Cisco industrial switches are rugged networking devices designed for harsh environments requiring high durability, security, and reliability.
[PDF Version]Contact us for competitive quotes on any of our power communication and smart grid products
Get a Quote