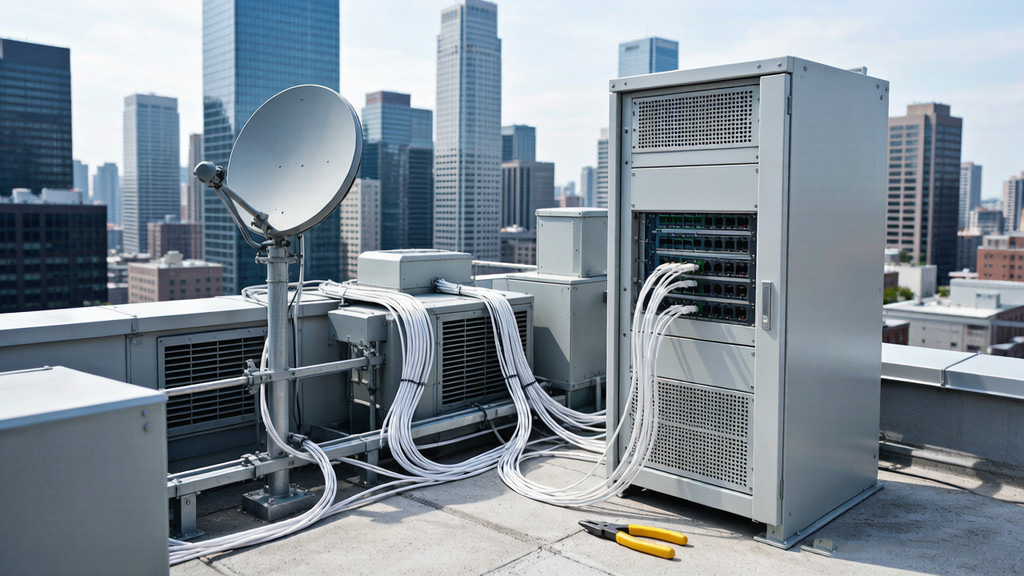
There are 8 steps to managing your network's security including: Be Organized. Develop and enforce a strong password policy. Ensure firewalls are properly configured. It implements security measures, policies, and tools that safeguard the entire network infrastructure to achieve the goal. This framework establishes best practices for device authentication, firmware updates, and real-time monitoring to detect potential threats. Develop data. This Security Requirements Guide (SRG) is published as a tool to improve the security of Department of Defense (DOD) information systems.
Low-voltage wiring, used in security cameras and internet networks, must follow specific safety rules to ensure it is installed correctly and safely. These rules are mainly outlined in the National Electrical Code (N.
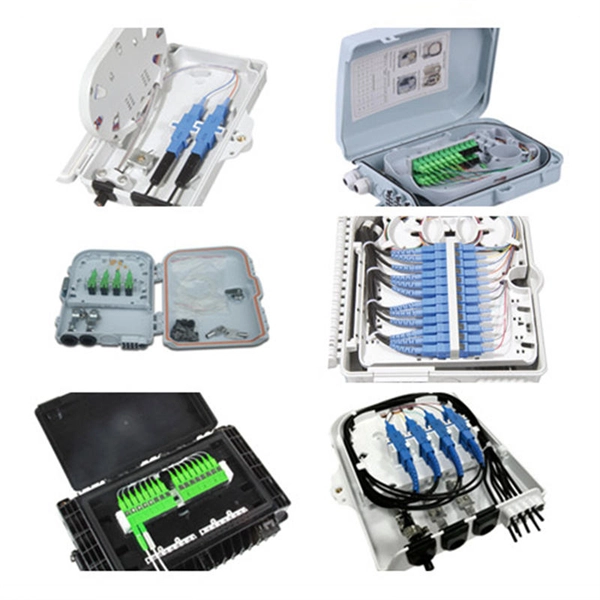
Key measures include securing network terminals, data centers, and access points with controlled entry systems, surveillance cameras, and fencing. Regular inspections and tamper-evident seals on fiber enclosures help detect unauthorized access or accidental damage early. Nowadays, the increasing reliance on fiber optic networks for transmitting vast amounts of data has brought about a pressing need for robust security measures to counter potential threats. In this fast-paced digital landscape, organizations must adopt a comprehensive approach to safeguarding their. In this blog, we will take an in-depth look at security measures for fiber optic communications, examining different strategies and technologies to ensure that data transmitted over this advanced infrastructure is intact and confidential. However, fiber is not invulnerable. Attackers with specialized tools can: Physically access unsecured junctions or cabinets.
[PDF Version]
This document provides the overall architecture for Deterministic Networking (DetNet), which provides a capability to carry specified unicast or multicast data flows for real-time applications with extremely low data loss rates and bounded latency within a network domain. ● Other distribution automation applications such as Direct Transfer Trip. Our engineers are experts at multifunction microprocessor-based relay technology, and we design protection schemes for generation, transmission, distribution, and low-volt ge systems worldwide. Of particular concern is the potential for cyberattacks that exploit high-wattage IoT devices, such as EV chargers, to manipulate local demand and destabilize the grid. With tools ranging from intent-based networking to policy-driven orchestration and multi-cloud integration, these leading. The handbook describes various power distribution system constructions and elements there-of, technical considerations, distribution automation infrastructure and functionality, communication aspects, special automation applications and life cycle aspects.
[PDF Version]
The SFP-10G-AOC SFP+ Active Optical Cable is a plug-and-play, cost-effective solution for 10Gbps connections. It uses Multi-Mode Fiber (MMF) with SFP+ connectors and has built-in optics, eliminating the need for separate transceivers and patch cables. DESIGNED FOR USE IN 10GB/S DATA RATE LINKS. COMPLIANT WITH 10G ETHERNET AND CPRI Amphenol's 10G SFP+ optical modules include SFP+ AOC. They are compliant with SFP+ MSA, SFF-8431 and SFF-8472, and are mainly used in Telecom, Wireless, InfiniBand, and Fiber Channel. AOCs are much thinner and lighter than copper cables, which makes cabling easier. 10Gtek. 10G SFP+ AOC (Active Optical Cables) are conceptually two SFP+ optical transceivers with a fiber optic cable permanently embedded into each end (the fiber cable cannot be removed). Whether you're upgrading server‑to‑switch links, extending. Pivotal Optics' Active Optical Cables (AOCs) are fully integrated, plug-and-play fiber assemblies designed for short- to medium-range high-speed data links—without the need for separate transceivers. Built with bonded multi-mode or single-mode fiber, these cables deliver secure, low-latency.
[PDF Version]
Network security audits help protect sensitive data by evaluating access controls, identifying security weaknesses such as open ports or outdated software, monitoring unauthorized activity, and ensuring compliance with data protection regulations such as GDPR or PCI DSS. This blog is about the top 10 network security testing methodologies that every cybersecurity professional should adopt in 2025. By learning and implementing these, organizations can strengthen their defenses and stay safe from attackers. The sophistication level of cyberattacks is staggering. public companies must disclose any cybersecurity incident they determine to be 'material' within four business days of that determination. Meanwhile, the average. Regular testing, integration with DevOps/CloudOps, combining automation with human expertise, and partnering with experts like Zymr, ensure enterprises stay resilient against evolving AI-driven and cloud-focused threats. Critical areas to focus on include evaluating firewalls, access controls, encryption methods, network segmentation, and patch management.
[PDF Version]
In this comprehensive guide, we'll walk you through each stage of the process, from understanding why business owners decide to sell, to preparing your company for the market, determining its value, finding qualified buyers, and managing negotiations through to closing. Selling your security systems installation business is a major decision, and knowing where to start can be challenging. Businesses often encounter challenges in handling excess technology, especially when it comes to pre-owned networking devices. Implementing best practices ensures that these devices are sold. Enterprises replacing networking hardware end up with surplus devices, including routers, switches, firewalls, and storage units. Holding onto these assets can occupy valuable space and tie up resources that could be better deployed. What you need is a network equipment.
Our hybrid powered cable transmits data and power in one cable, ideal for powering security cameras, Wi-Fi access points, and more, eliminating the need for separate data and power lines. Uninterrupted monitoring of large infrastructure for increased safety and targeted preventative maintenance. Various cable constructions within the portfolio offer unlimited. CommScope bundles hybrid cabling to your custom specifications, using our high-performance fiber-optic, unshielded twisted pair and coaxial cables. ActiFi is a Class 3‑rated composite cable that supports low‑voltage (Class 2, 57 VDC/100 V) as well as bulk power solutions.
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. This guide evaluates the 10 best network security solutions for 2026, detailing technical specifications, key strengths, purchase rationale, and unique capabilities for global enterprises, mid-market growth companies, and hybrid workforces.
You'll get the precise, standardized dimensions of a 1U server rack unit — including height (1. 45 mm), width (19″ / 48. 26 cm), mounting hole spacing, and critical clearance allowances — plus actionable guidance on verifying physical fit, avoiding common installation. The IPC-C1E-BAR30-RH-N1 is an entry-level 1U appliance chassis with 15” depth for space-sensitive applications, such as Network & Security appliance, firewall, VPN, Telephony and military applications. 6” x 12”) motherboard can be populated into this appliance chassis. reserves the right to make any final modifications. For example, a typical full-size rack cage is 42U high, while equipment is typically 1U, 2U, 3U, or 4U high.
Contact us for competitive quotes on any of our power communication and smart grid products
Get a Quote